


Latest Product Releases
Explore the platform that keeps evolving to stay ahead of fraud. Every release adds clearer signals, faster investigations, and more context with actual intelligence, so your team can make confident decisions faster and with less second-guessing.

Meet the Attack Detection Agent:
The First Part of Sift’s Fraud Attack Defense Suite
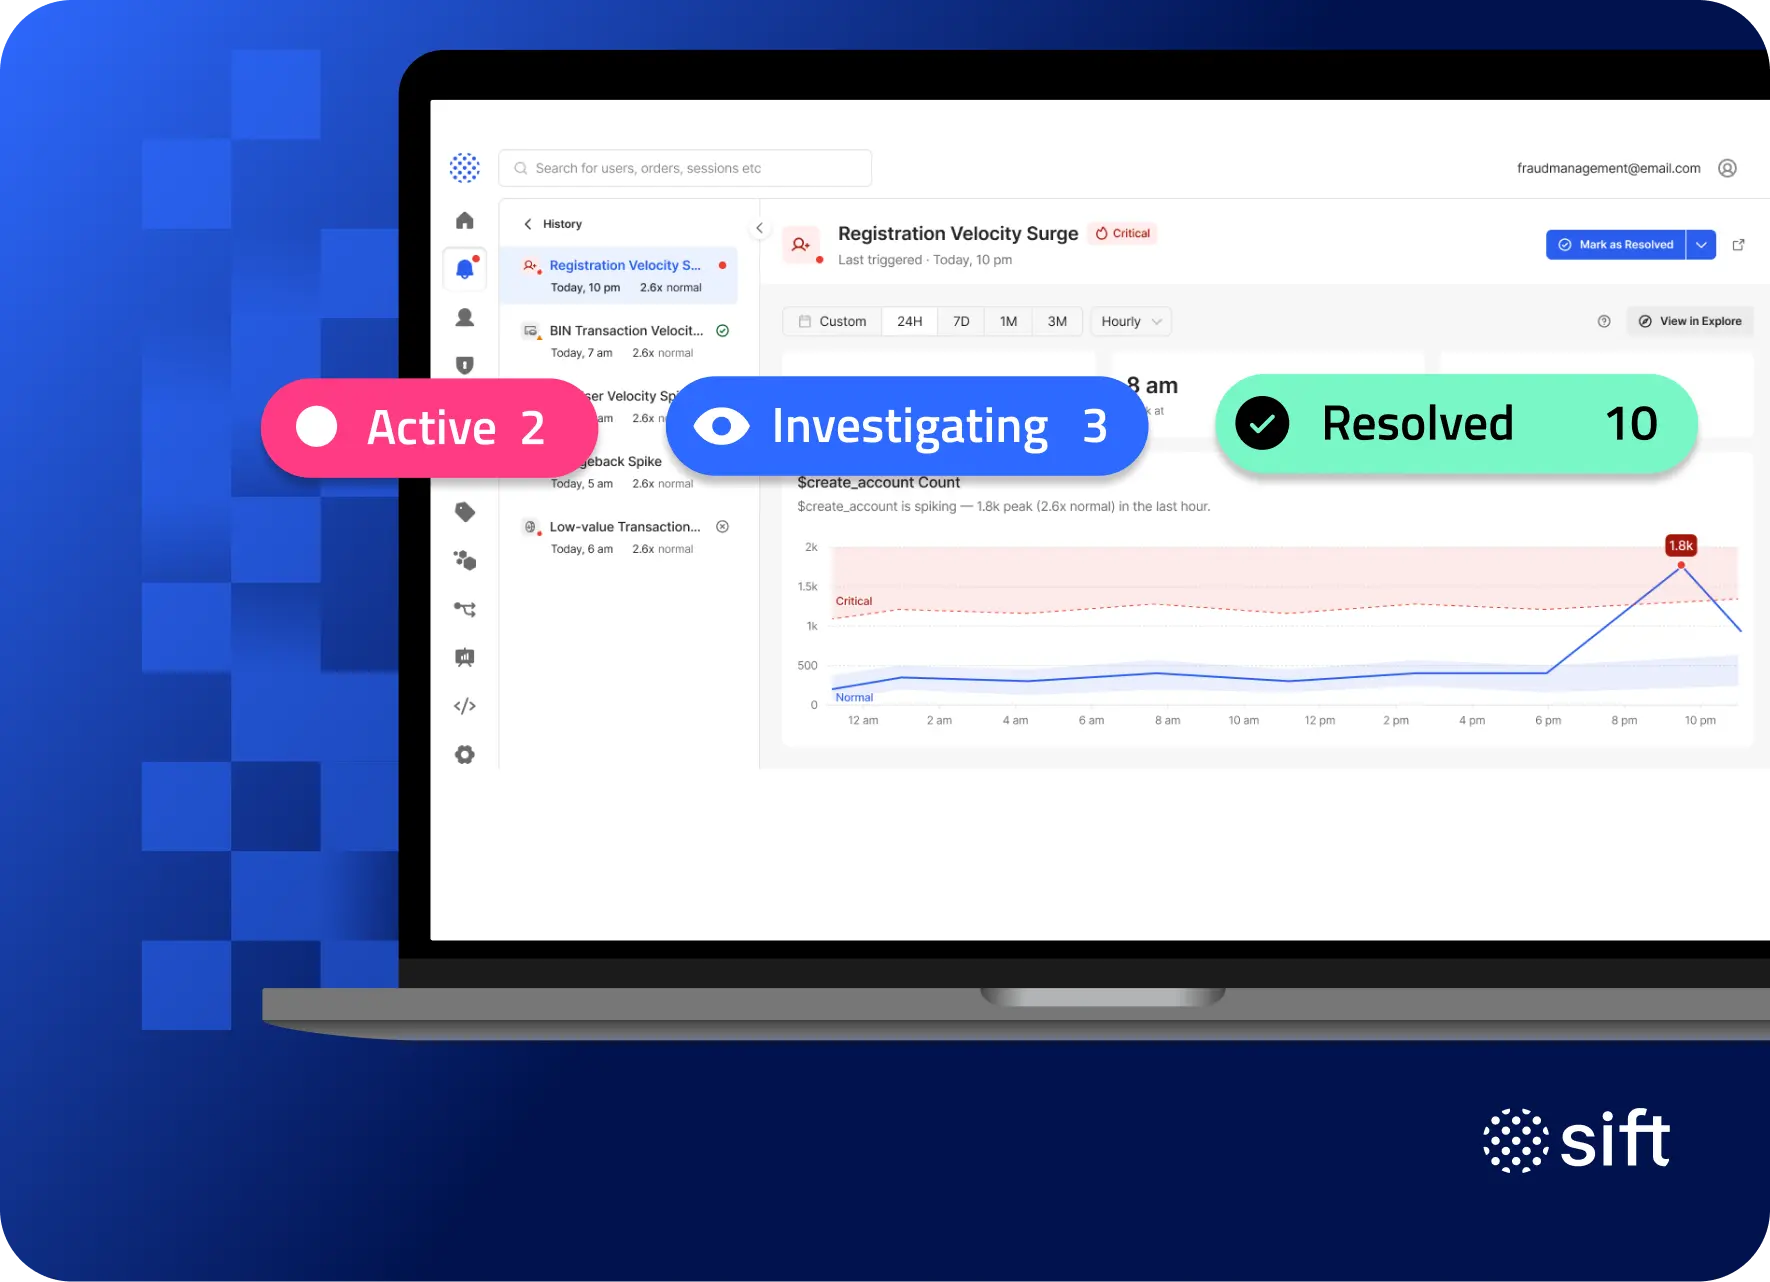
Attack Lifecycle
THE SOLUTION
Get end-to-end visibility into every alert, from detection to resolution, so your team can act faster.
HOW IT WORKS
A unified timeline tracks every status change (Open, Acknowledged, Resolved, or False Positive) with full audit logs and ownership records. Teams see the full lifecycle without leaving the Sift Console.
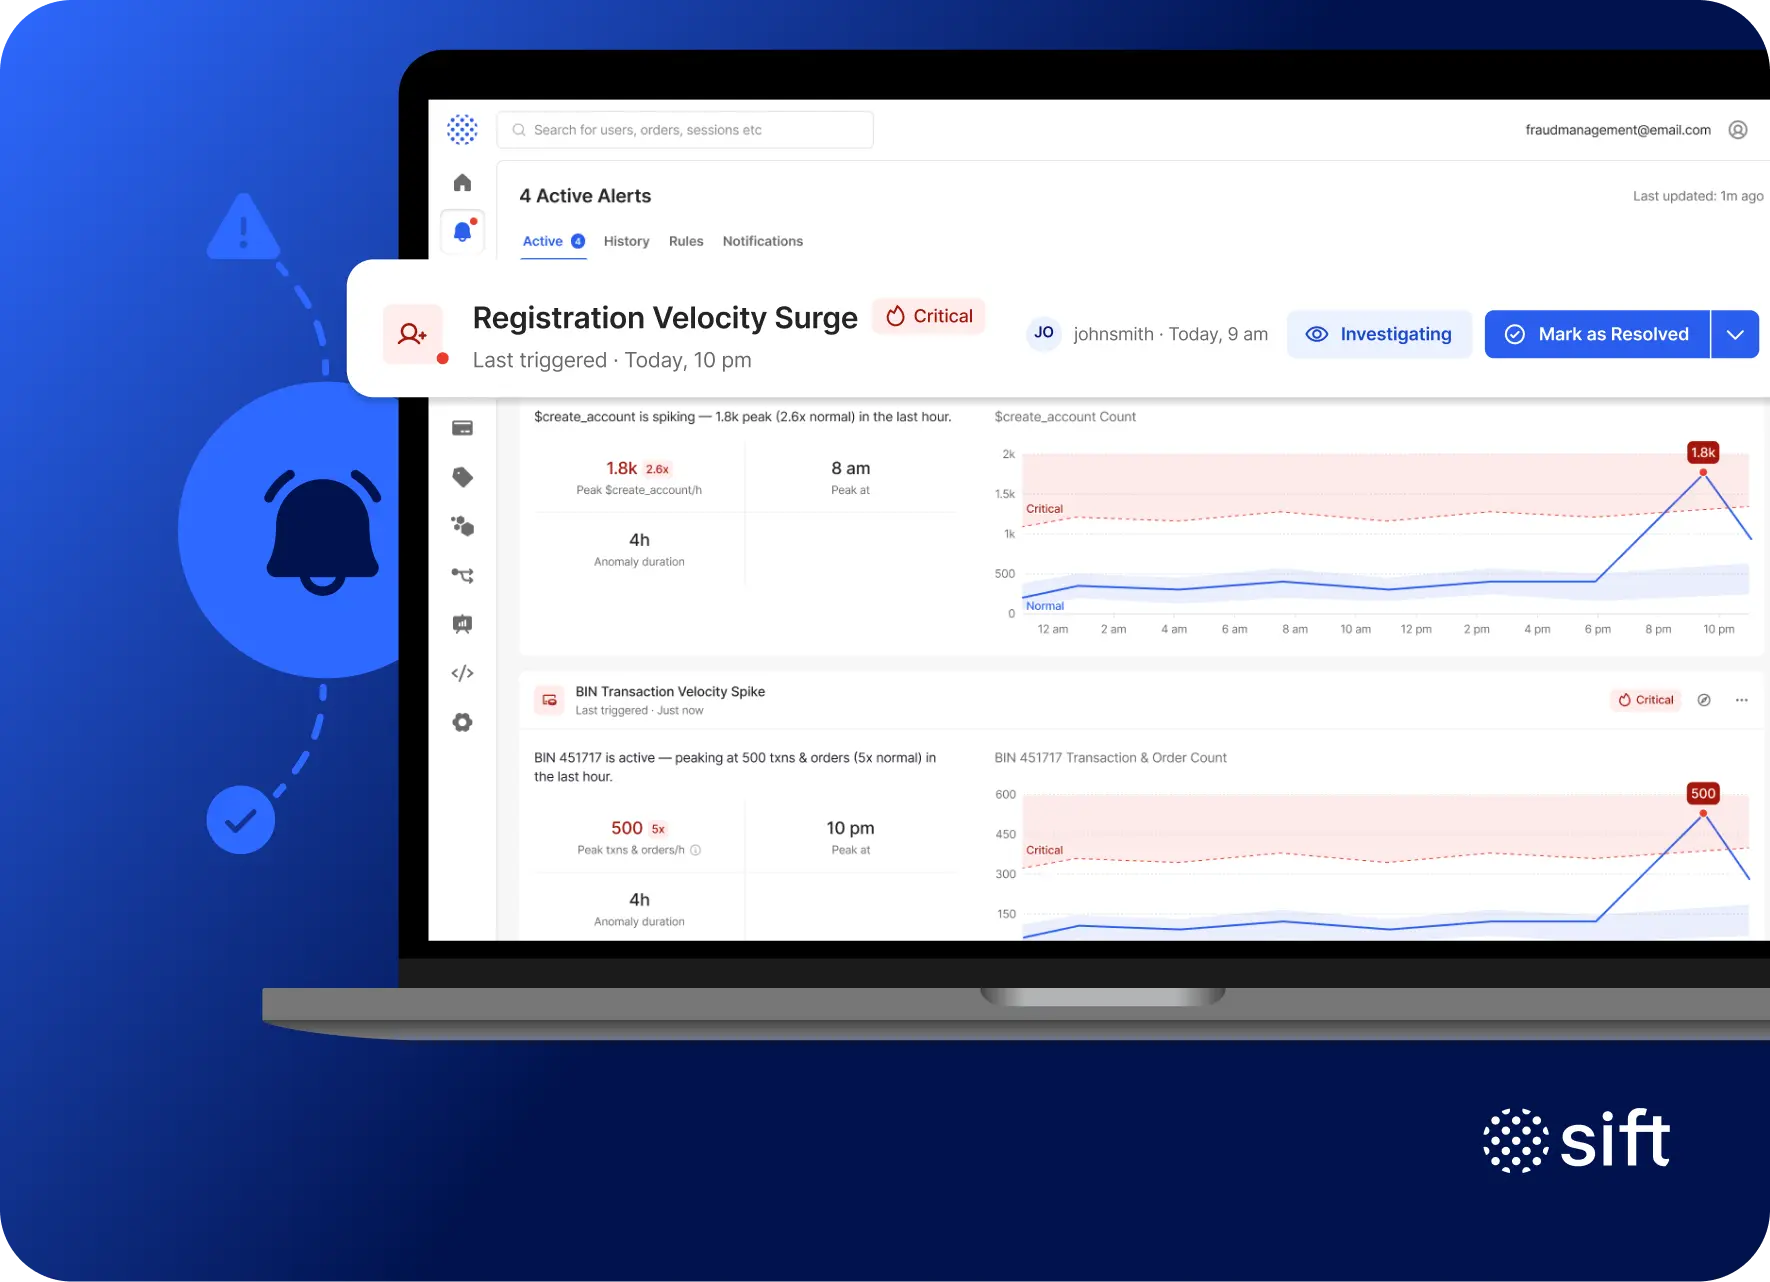
Attack Visualization
THE SOLUTION
See exactly what triggered an alert, with charts showing how activity deviates from your normal baselines.
HOW IT WORKS
Time-series charts plot the threshold, the deviation, and your key metrics side by side, with the anomalous point marked. Analysts can see exactly where normal ended and the attack began.
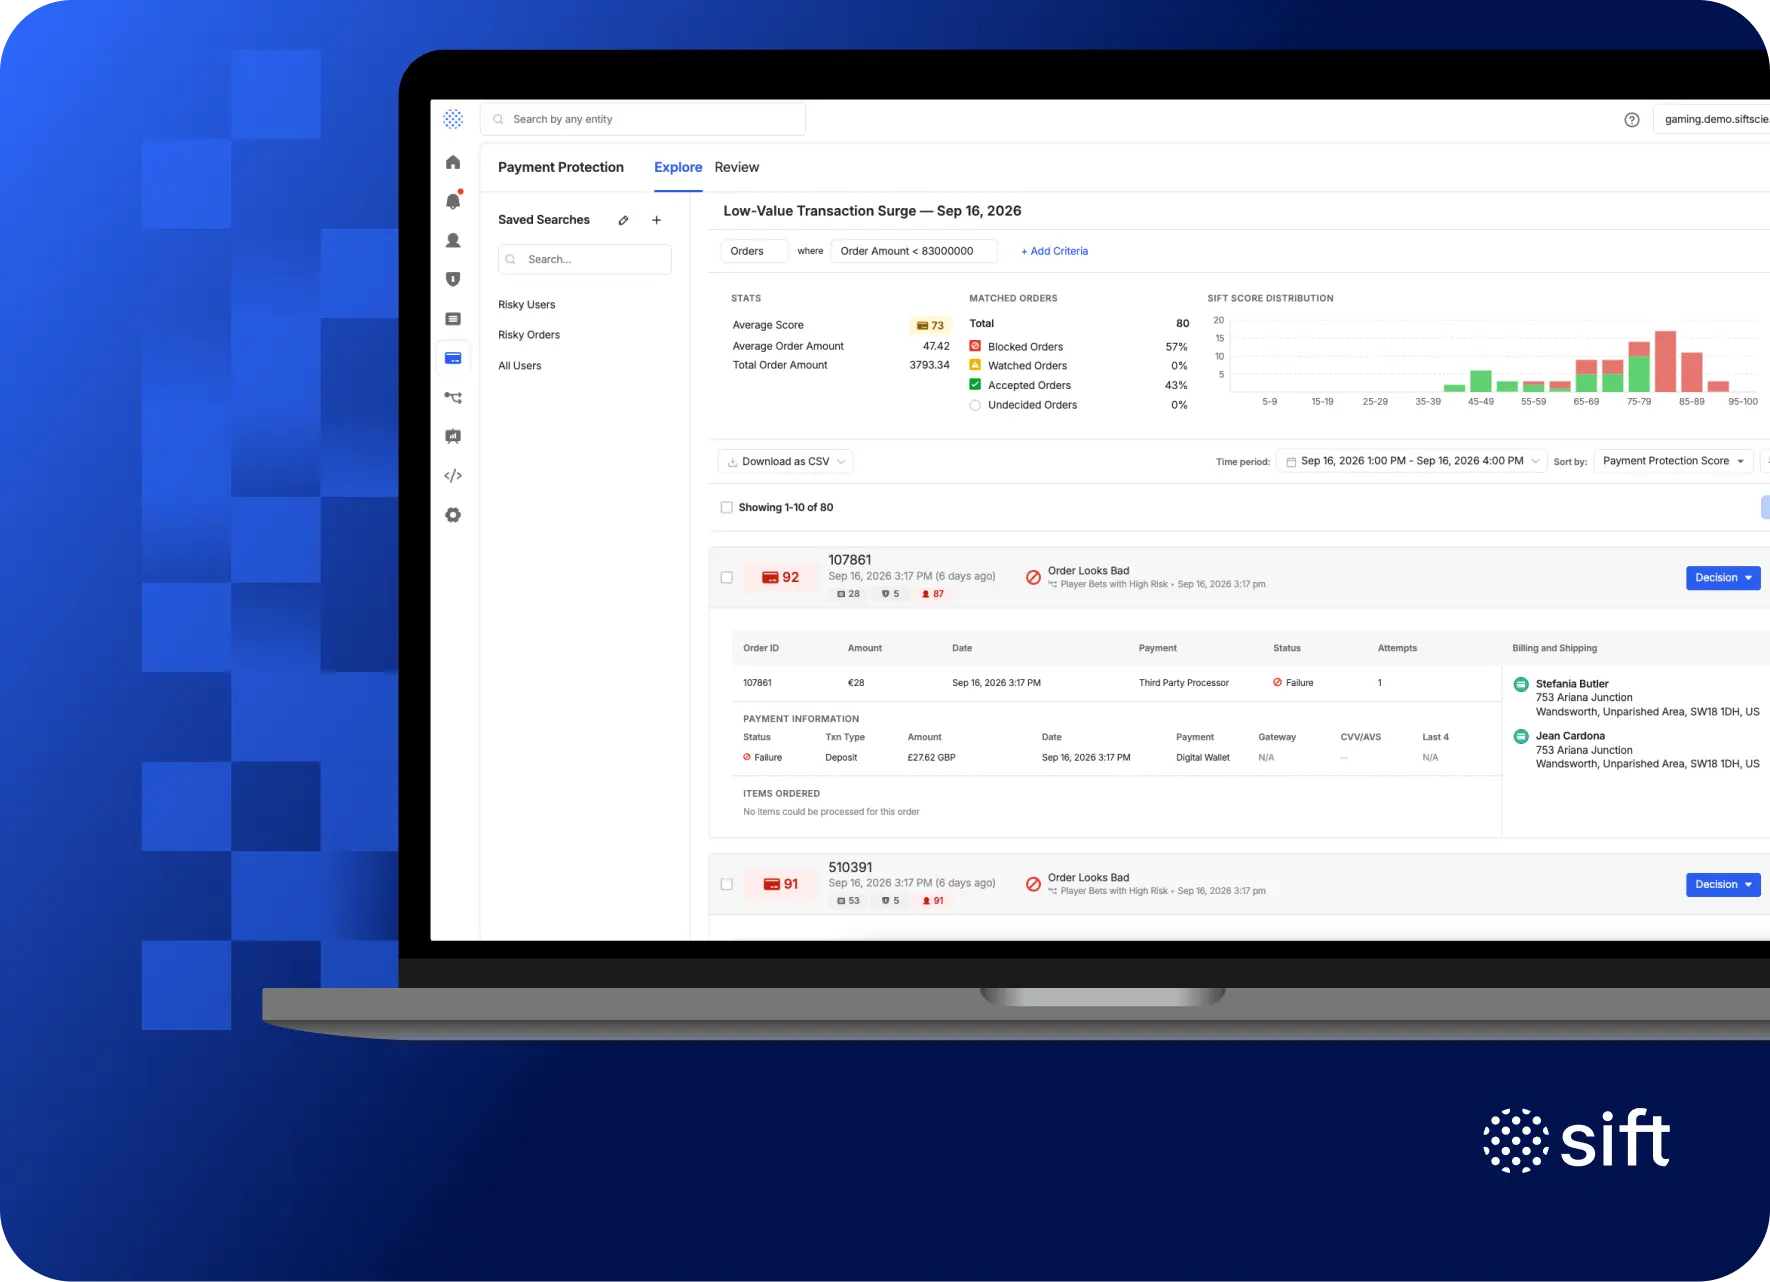
Investigation, Starting Today
THE SOLUTION
Jump from any alert straight into a deep-dive investigation in Explore, without losing any context.
HOW IT WORKS
One click from any alert takes analysts into Explore, pre-filtered to the exact cohort, time range, and scenario. Investigators start on the pattern, not on setup, with every matched event in one view.
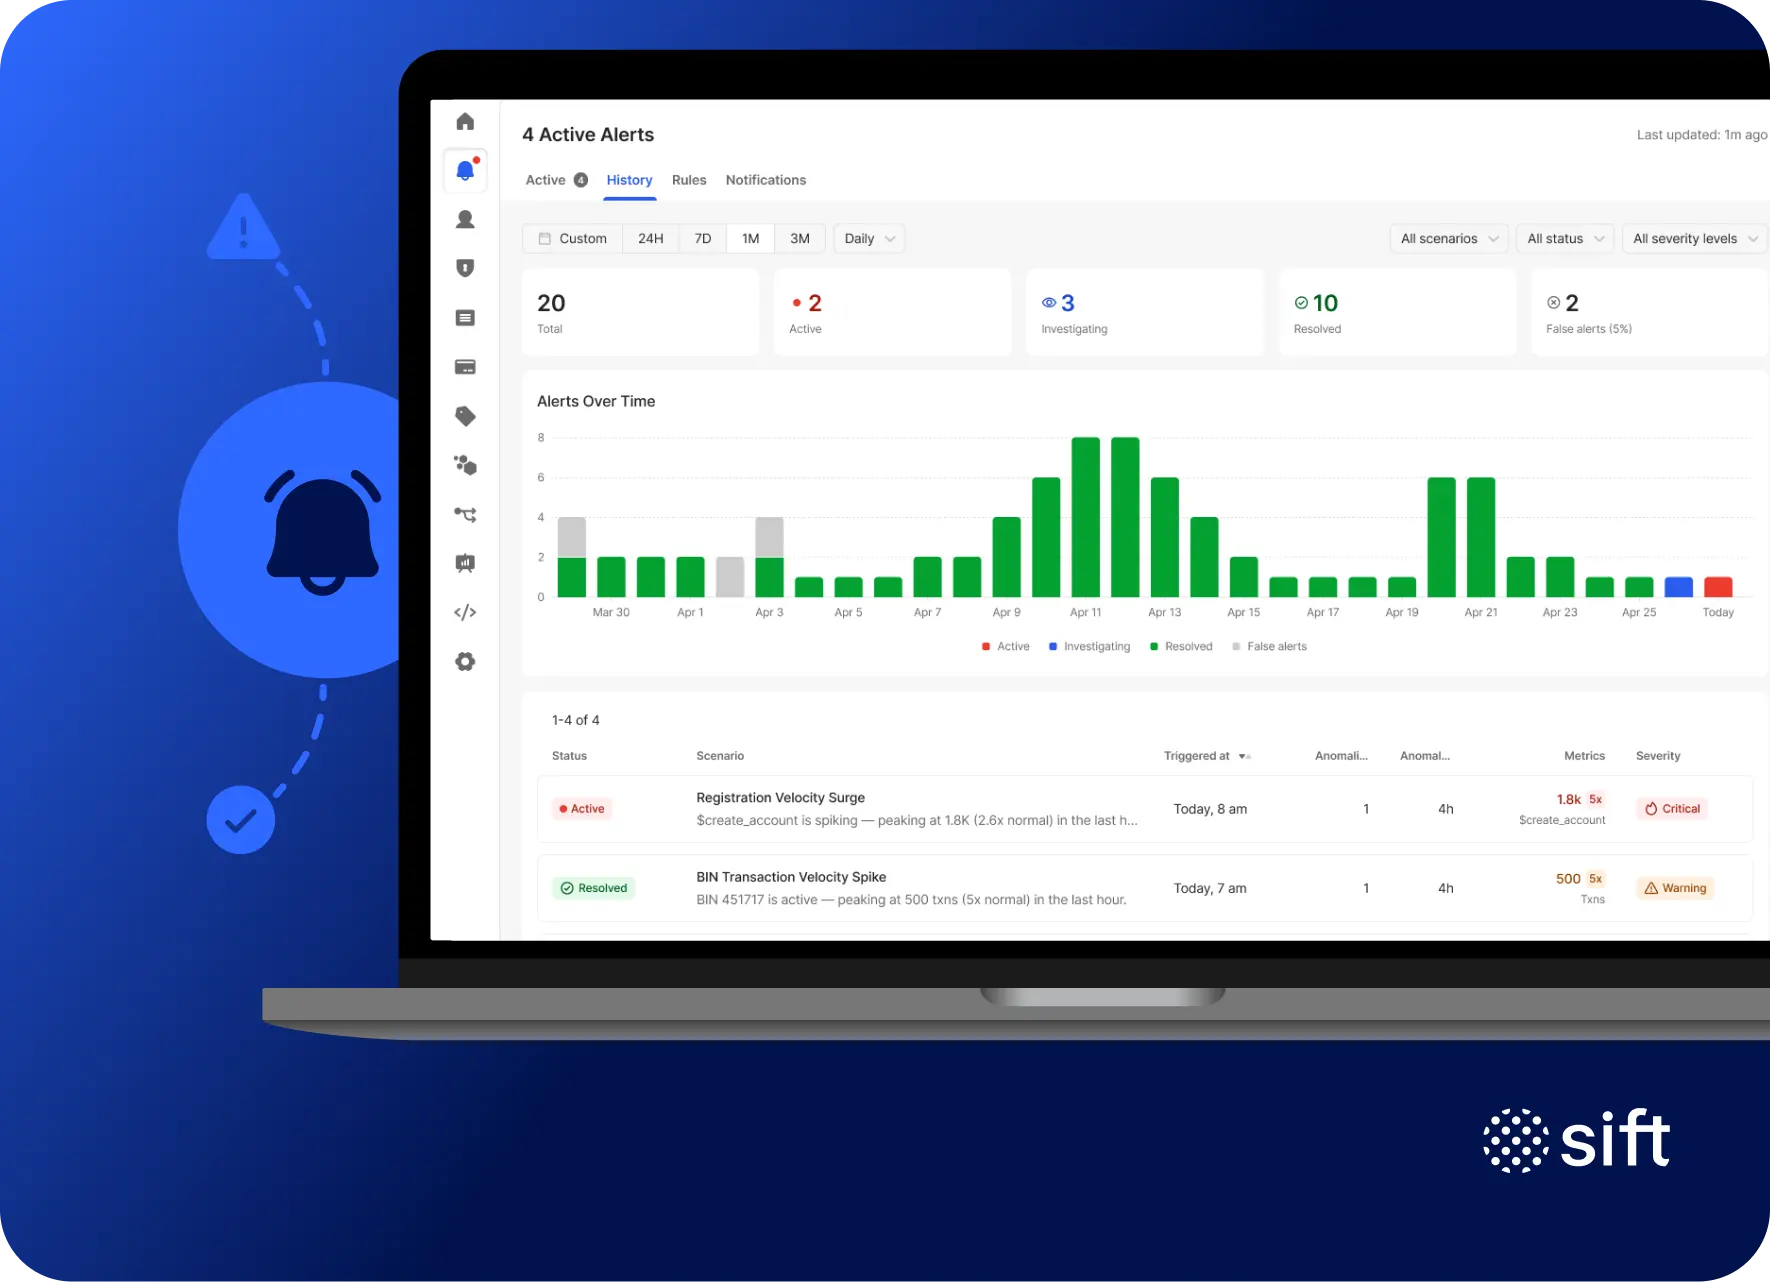
Attack History
THE SOLUTION
Keep a persistent, searchable record of every alert and the decisions made on it for audit and review.
HOW IT WORKS
Every status change, ownership transfer, and analyst action is logged with timestamps and user attribution, giving your team a clear, complete record for compliance and post-incident review.
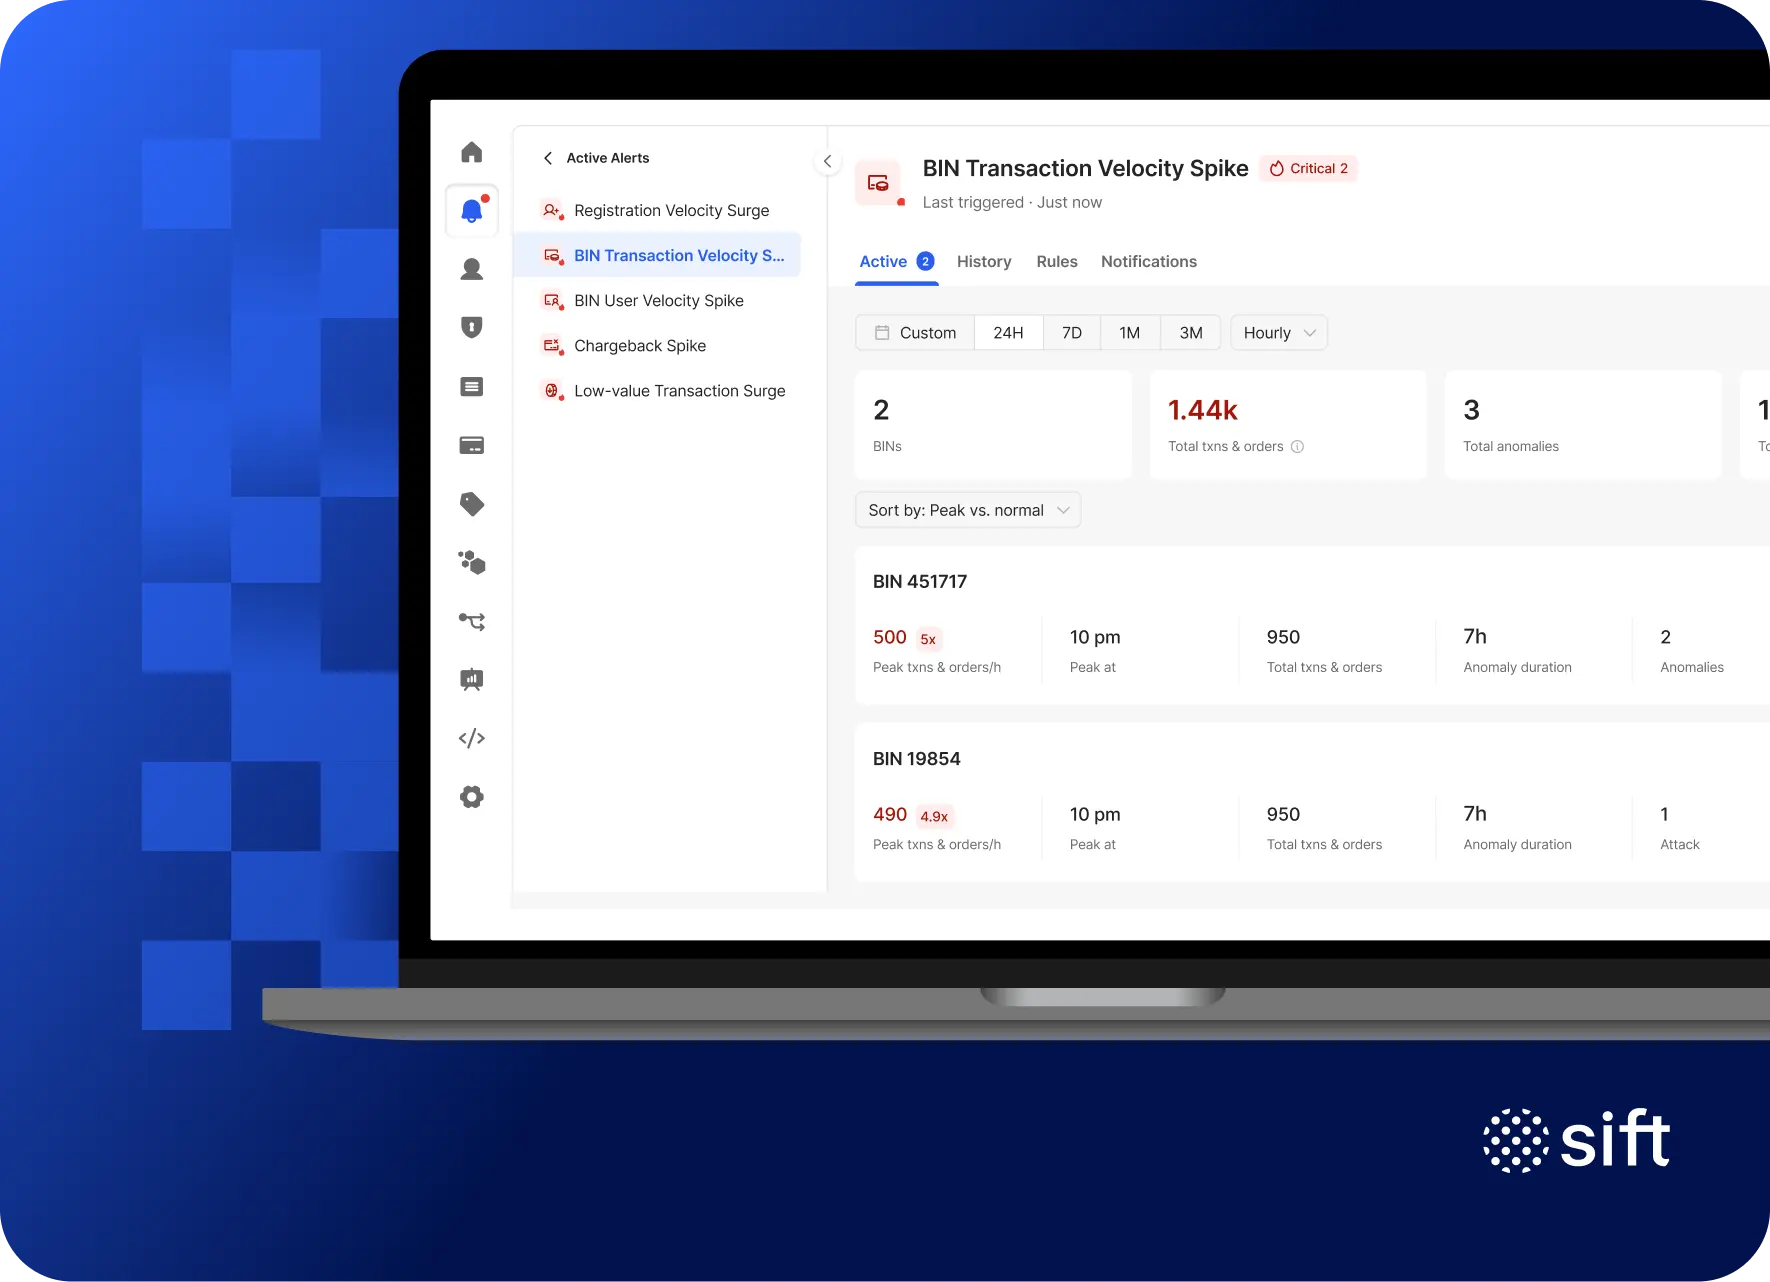
One Attack, One Alert
THE SOLUTION
Related detections across BINs group into a single alert, with individual BIN detail still one click away.
HOW IT WORKS
When multiple BINs trigger the same attack pattern in one window, Sift groups them into one alert instead of flooding the queue. Analysts work one batched investigation, not several separate ones.
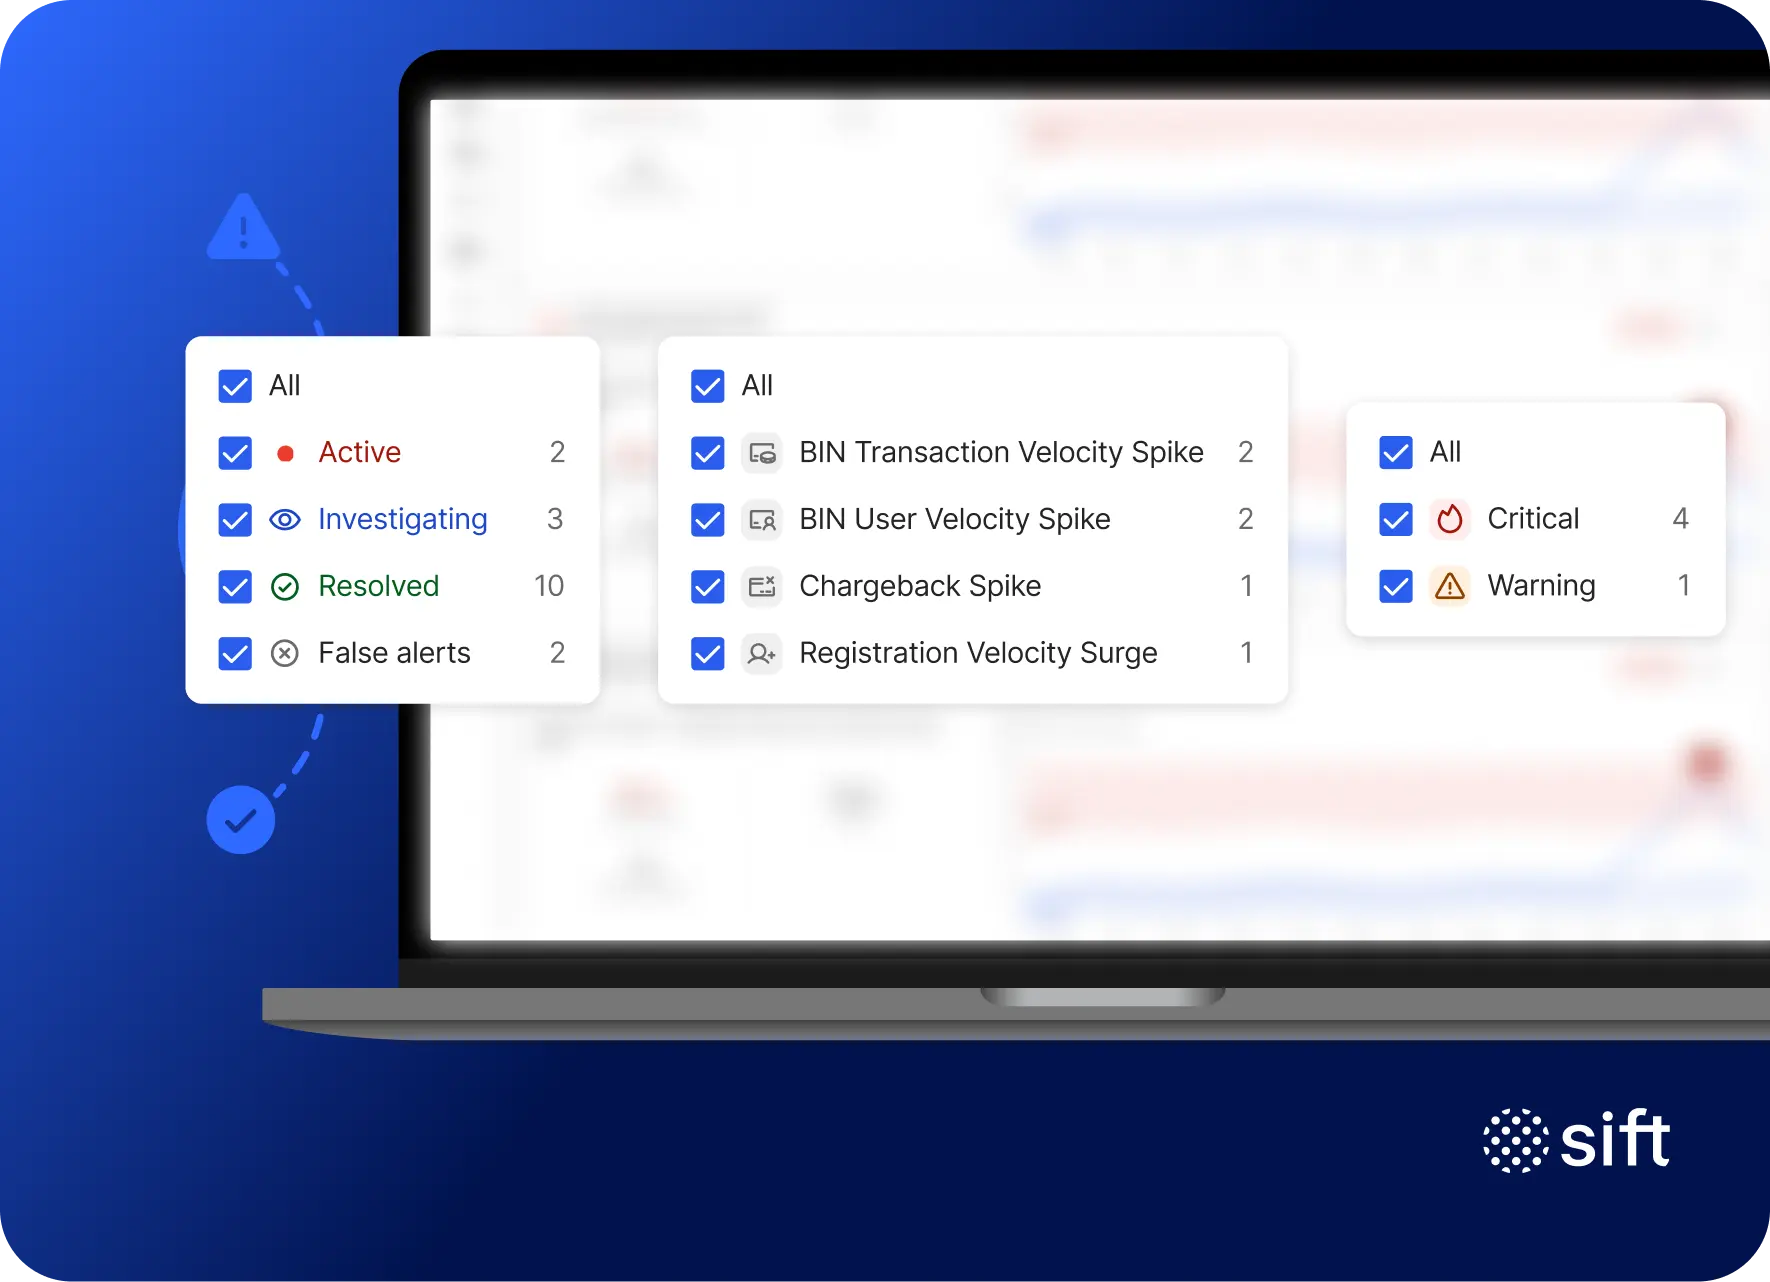
Advanced Filters
THE SOLUTION
Filter the alert feed by time and scenario type, so teams can zero in on what matters most to them.
HOW IT WORKS
Combine time and scenario-type filters in any configuration to narrow the alert feed to exactly what you're investigating, whether that's one BIN attack or a week of registration surges.
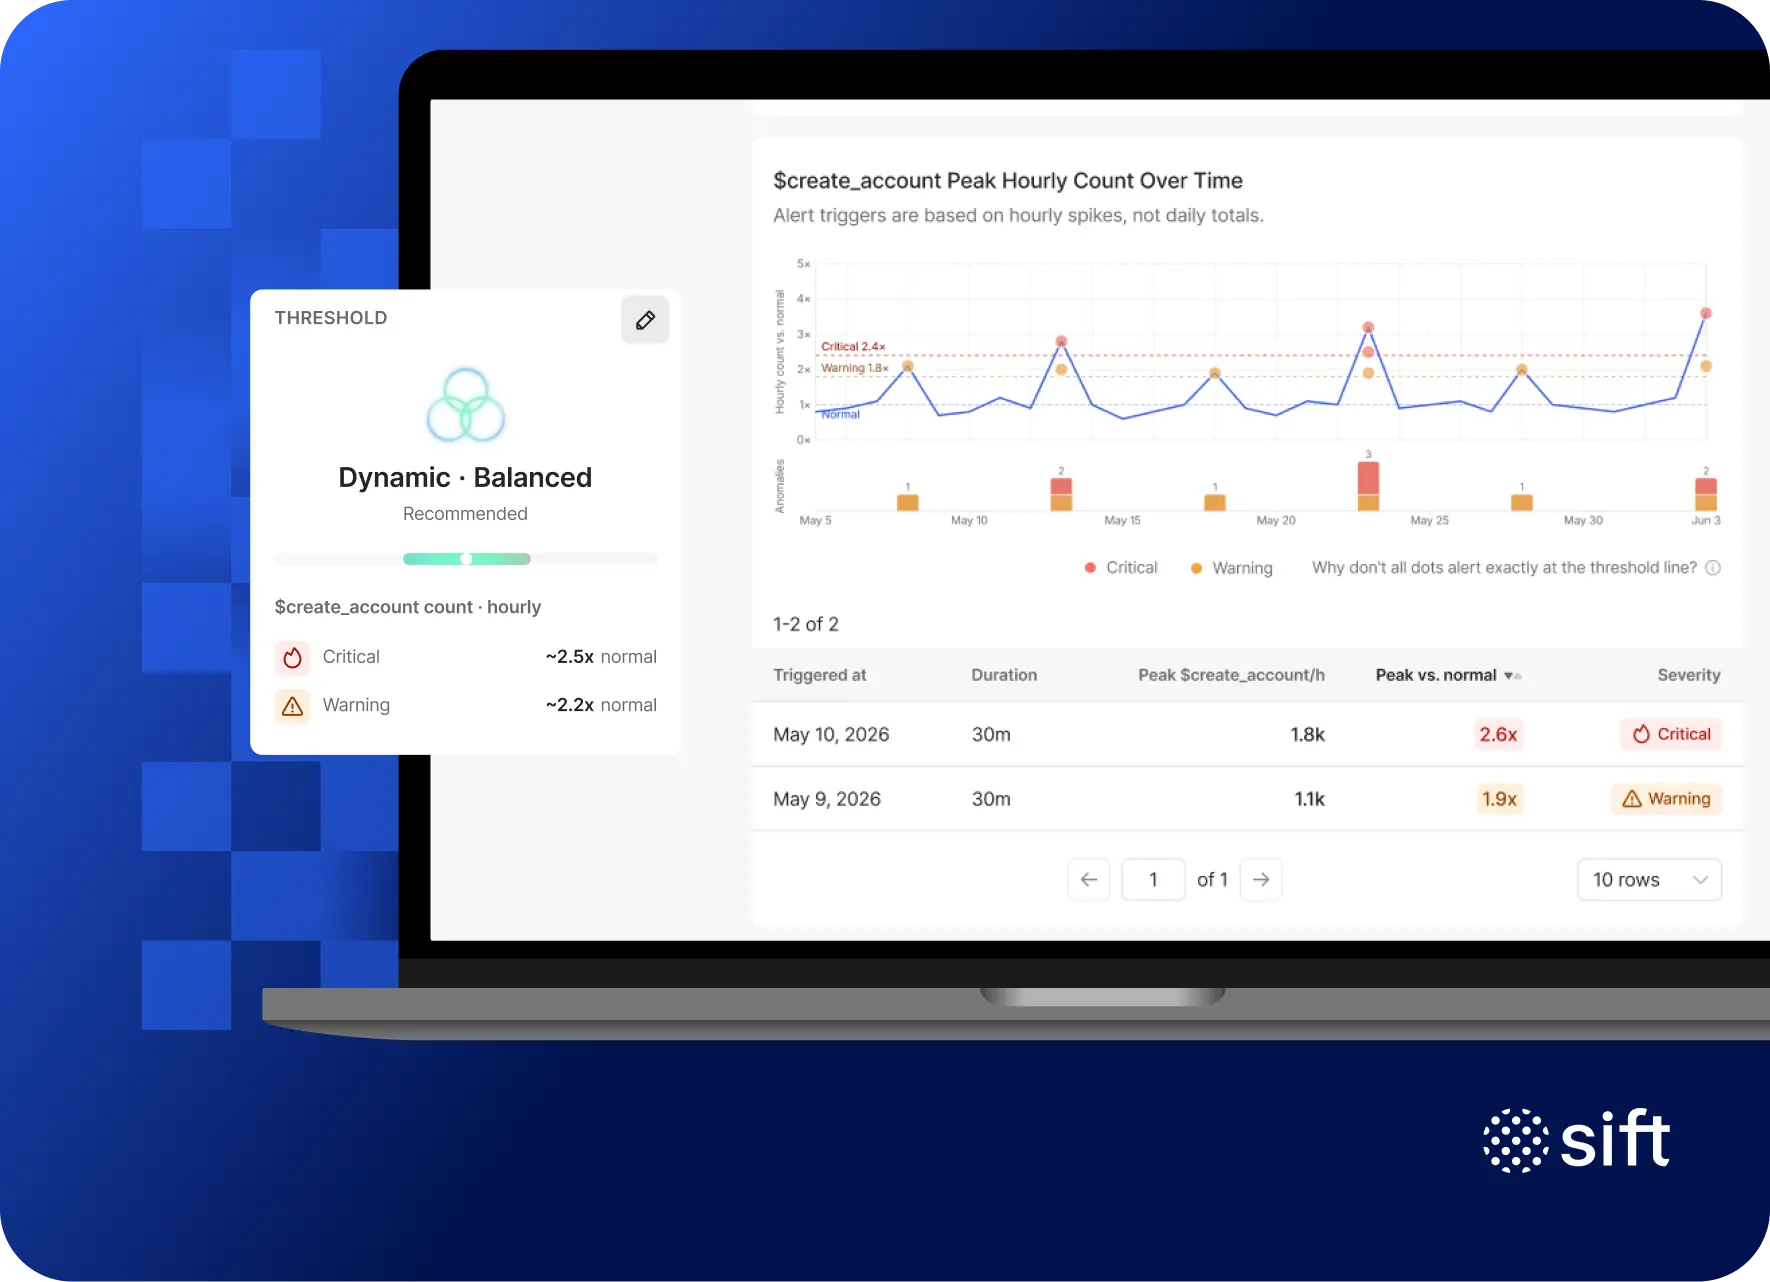
Attack Sensitivity
THE SOLUTION
Use pre-calibrated thresholds based on industry benchmarks, or set your own to match your risk tolerance.
HOW IT WORKS
Detection runs on Sift-defined thresholds tuned to time-of-day and day-of-week patterns, so a busy Monday morning doesn't trigger a false alarm. Want more control? Adjust thresholds to what works for you.
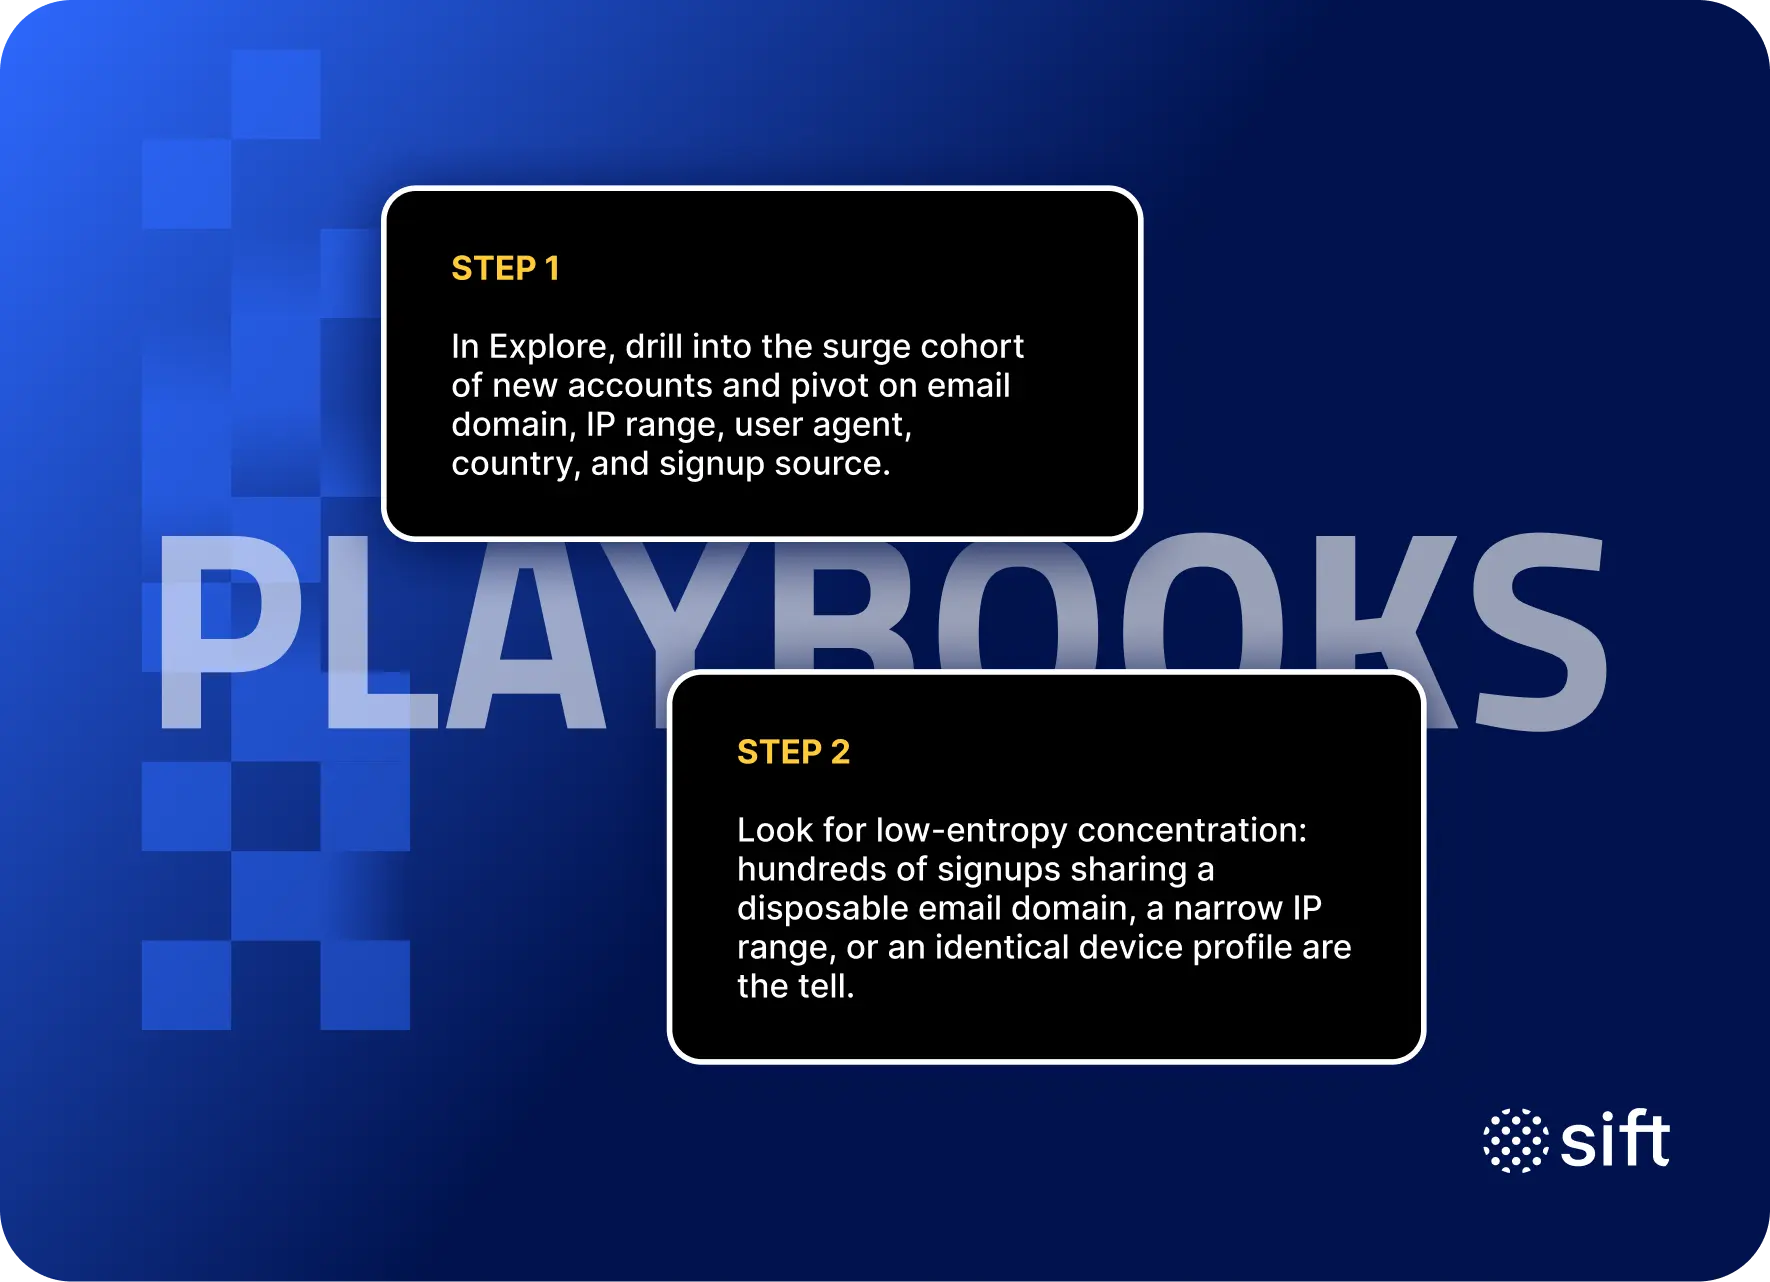
Investigation Playbooks
THE SOLUTION
Get step-by-step, prescriptive guidance built into every alert, so no one starts from a blank page.
HOW IT WORKS
Each alert type comes with a tailored playbook: drill into cohort attributes in Explore, spot low-entropy clusters, and confirm the attack. New analysts ramp faster, and expert know-how scales to the whole team.
Explore More Capabilities
Smarter Fraud Decisions & Faster Operations
Global Profile Intelligence keeps network identity links fresh and surfaces cross-network context in the Console, Workflows, and Explore, so analysts recognize trusted users faster and act with confidence. New attack and anomaly detection alerts teams when key metrics move outside expected baselines, with clear investigation paths attached. Stronger device and login visibility, including more persistent iOS Device IDs and FIBR In-Console benchmarking for Account Defense, helps catch account takeover earlier. Bulk commenting, the Workflow Lists API, and advanced data export cut manual work and speed up daily operations.
Advanced Fraud Intelligence & Operational Excellence
ActivityIQ is a GenAI fraud research assistant that summarizes user actions across sessions in seconds, helping teams spot high-risk activity faster and reduce investigation time. FIBR-In-Console delivers instant benchmarking by showing company metrics side-by-side with industry and global fraud rates. With Automatic Chargeback Labeling and smarter Console upgrades, analysts gain sharper accuracy, less manual work, and faster day-to-day operations.
FIBR In-Console: Fraud Benchmarking at Customers' Fingertips
FIBR in-console makes it easier for customers to gain a deeper understanding of fraud performance relative to industry and global benchmarks. Now, a company’s unique chargeback and block rates are pre-populated right alongside FIBR data directly within the Sift Console, offering a clear, side-by-side view of attack rates and vertical-specific insights.
Precise, Powerful Insights & Unified Account Takeover Operations
Sift’s enhanced ATO solutions combine identity-centric accuracy, real-time behavioral analysis, and device fingerprinting to detect account takeover fraud faster and more precisely, eliminating data gaps and delayed response. With seamless CIAM integrations, fine-tuned MFA controls, and pre-built automations, businesses gain actionable insights and unified workflows that prevent a median of up to $4.2 million per year in fraud losses per customer.
Revolutionizing Fraud Detection with Industry-Specific Consortium Models
ThreatClusters is a revolutionary approach to risk decisioning that uses a multi-pronged method, combining the precision of customer-specific risk models with the broader intelligence of a global model, in order to derive risk signals that are unique to each industry. ThreatClusters can improve fraud decision accuracy, reducing the risk of false positives/negatives up to 20% by fine tuning risk models to incorporate the real-time behavior traits of a cohort of peers, in addition to new-to-cohort fraud patterns.
Intelligent Cruise Control for Fraud & Risk Operations
RiskWatch makes it possible to set target block rates that automatically adapt in response to changes in user behavior, fraud attacks, or other dramatic shifts. RiskWatch automatically accounts for changes in user behavior patterns in real time, during fraud attacks or other dramatic shifts, with block rates adapting to capture additional risky events as they occur. As attacks conclude, risk thresholds return to pre-fraud levels that can be easily adjusted.
Patents
With more than 40 patents and counting, Sift has built an ongoing track record of trust for every business in its network.

Innovate Beyond Traditional Fraud Prevention
Combine global intelligence with clear, configurable control to approve more trusted customers, reduce operational burden, and scale securely.