




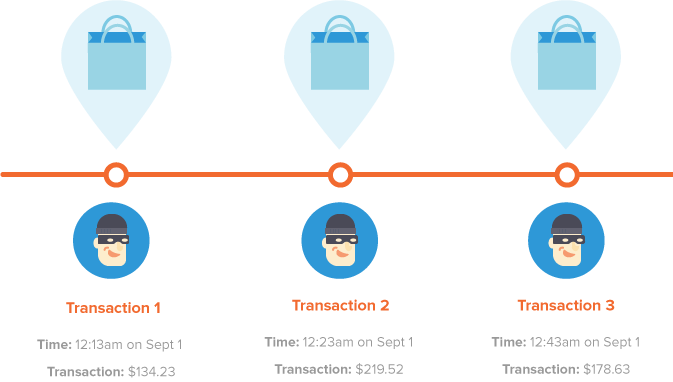
If fraudsters were content to place a single order and then leave the targeted merchant alone, they would be less of a nuisance but much harder to detect. Looking at patterns of how different transactions are related in time can help highlight which orders are riskier than others.
Basic velocity check: How much money has this customer spent in the last day?
The simplest pattern to look for is, “How much activity has User X had lately?” Combinations of signals may point broadly to common fraud patterns. For example, conducting three or more transactions in the space of an hour might, for a given business, be something that most fraudsters do but legitimate customers rarely do. Dollars spent, rather than a count of orders placed, can be used as well.
Potentially Fraudulent Behavior
You may want to track activity by something other than account, as well. Merchants can track how many transactions have come from a single device in a day, for example, or how many orders have been placed with a particular shipping address. Other attributes that a merchant may want to track the velocity of include email address, phone number, and credit card number. One attribute that could present too much noise would be an IP address since many legitimate users could be coming from the same IP. Another strategy is to combine different attributes to reduce noise. For example, only flagging transactions that share the same device AND email domain.
Advanced velocity check: How many accounts have been seen on this IP address in the last 30 days?
It’s somewhat more technically tricky to track, but another strong signal is “How many unique instances of X have been seen that have Y in common in period of time Z?” One example of this might be how many unique accounts have placed orders sharing a single IP address in the last 30 days. There are a few ways to do this programmatically on the front end, and many fraud services do it by default. Again, the key is to find which signals are most closely tied to fraud.
If you can, experiment with different measures of velocity and monitor which most clearly differentiate trustworthy orders from suspicious. Some starting points for things to count (and to count by) are:
- User ID / Email / Email domain
- Device Signature
- IP Address
- Browser Cookie
- Shipping Address
- Billing Address
- Payment Method
- Item being purchased (e.g. gift cards)
In general, anything that you would be surprised to find that two users share is a good velocity to look into. If you have a loyalty program or are running a promotion, for instance, you might get a useful signal out of how many different billing zip codes have been seen sharing a loyalty number in the past month.
Choosing the right time window
A velocity check is only as useful as the window it measures. Three orders in an hour means something very different from three orders in a month. Short windows, such as one minute to one hour, catch bursts like card testing and fast account takeover attempts. Longer windows, such as one day to 30 days, catch slower patterns like one device cycling through many accounts.
Most teams run the same velocity across several windows at once, for example one hour, 24 hours, and seven days. Compare the counts against what your own customers do, since a food delivery app and a furniture retailer have very different baselines.
Combining velocity signals to reduce false positives
Any single velocity is blunt. Households share IP addresses, offices share devices, and a customer buying holiday gifts may ship to several addresses in a short time. Flagging on one count alone catches those customers along with the fraudsters.
Pairing signals narrows the target. A device linked to five accounts is a lead, but a device linked to five accounts that also share an email domain and placed orders all within the same hour is far more convincing. When a case lands in a gray area, route it to manual review or step-up verification instead of an automatic decline, so a real customer can still get through.
Velocity checks across common fraud types
Velocity thinking applies well beyond checkout:
- Card testing: Counting distinct cards or failed attempts per device or IP address over a few minutes exposes fraudsters probing stolen card numbers.
- Account takeover: A burst of failed logins across many accounts from one device points to credential stuffing.
- Fake account creation: Many sign-ups sharing a device, email domain, or phone number in a short period often signal automation.
- Promo and policy abuse: Many accounts redeeming one offer from the same device or shipping address is a classic sign of multi-accounting.
Where velocity checks fall short, and how to tune them
Fraudsters know velocity checks exist. Bots can spread activity across rotating IP addresses, many devices, and long gaps between attempts, which keeps each individual count below your threshold. That is why velocity works best as one signal among many, weighed alongside device, behavioral, and network signals by machine learning models that adjust as attackers change tactics.
Start with two or three velocities tied to the fraud you already see. Run new checks in a monitor-only mode, compare flagged orders against confirmed outcomes, and tighten or loosen thresholds before any of them trigger blocks. Revisit them each quarter and around peak periods like holiday sales, when normal behavior shifts.
Velocity checks catch a lot, but fraudsters adjust to them. See how Sift weighs velocity alongside device, behavioral, and network signals to catch what a single count misses, without slowing down legitimate customers.
Frequently asked questions
What is a velocity check in fraud detection?
A velocity check measures how often something happens within a set period, such as orders per device in an hour or unique accounts per IP address in 30 days. Unusual speed or volume can signal fraud.
What velocity threshold should I use?
There is no universal number. Look at how often legitimate customers hit a given count in a given window, set thresholds above that normal range, and test them against confirmed fraud.
Can velocity checks flag legitimate customers?
Yes they can, especially when only a single signal is used on its own. Combine attributes, use longer windows for weak signals, and send borderline cases to review instead of declining outright.